DEF CON 34 Is Here: A Look Back at 33 Years of Bugs That Changed Security Forever
DEF CON 34 has kicked off in Las Vegas under this year's theme, "Agency." From Back Orifice to ATM jackpotting and the remote Jeep Cherokee hack, here's how 33 years of stage-dropped disclosures rewrote the security playbook — and what they mean for your business today.
By Tom Brennan
Today, the air inside the Las Vegas Convention Center West Hall is thick with soldering smoke, high-end packet captures, and the quiet hum of thousands of laptops running Kali Linux. DEF CON 34 has officially kicked off. The theme this year? "Agency": a sharp look at who controls the digital systems we live inside, self-determination in tech, and what happens when AI agents gain excessive autonomy without human oversight.
For over three decades, DEF CON hasn't been your average corporate trade show with carpeted booths and vendor pitch decks. It's the annual family reunion of the world’s sharpest security practitioners, researchers, and builders.
Let’s take a walk down memory lane to see how a small farewell party in 1993 morphed into the crucible of modern cybersecurity, and why the flaws disclosed on these stages changed the way the world builds software and hardware.
From a 1993 Farewell Party to the World's Largest Hacker Con
Back in the summer of 1993, Jeff Moss (known in the underground as The Dark Tangent) organized what was supposed to be a simple farewell party in Las Vegas for a retiring member of the Fidonet hacking community. Around 100 hackers showed up at the Sahara Hotel and Casino. They drank beer, plugged dial-up modems into hotel phone jacks, and swapped floppy disks.
They didn't know it yet, but they had just birthed DEF CON.
Over the next thirty-three years, the conference evolved at breakneck speed:
- 1996 (DEF CON 4): The introduction of the first Capture The Flag (CTF) competition, setting the gold standard for global hacking battles where teams defend their own servers while attacking others.
- 2004: Launch of the legendary Black Badge program, honoring winners of official contests with the most coveted prize in security.
- 2008: A pivotal shift as federal agencies (NSA, DHS, FBI) began openly attending, speaking, and recruiting, bridging the ancient divide between underground hackers and national defense.
- 2017: DEF CON outgrew its historical hotel venues and moved into the massive Las Vegas Convention Center.
- 2020: The legendary virtual "Safe Mode" year during COVID-19, proving the community could hack from anywhere.
- 2026 (DEF CON 34): Today, cash-only at the door ($520), tens of thousands of attendees, and the "Agency" theme setting the tone for the next era of AI and automation security.
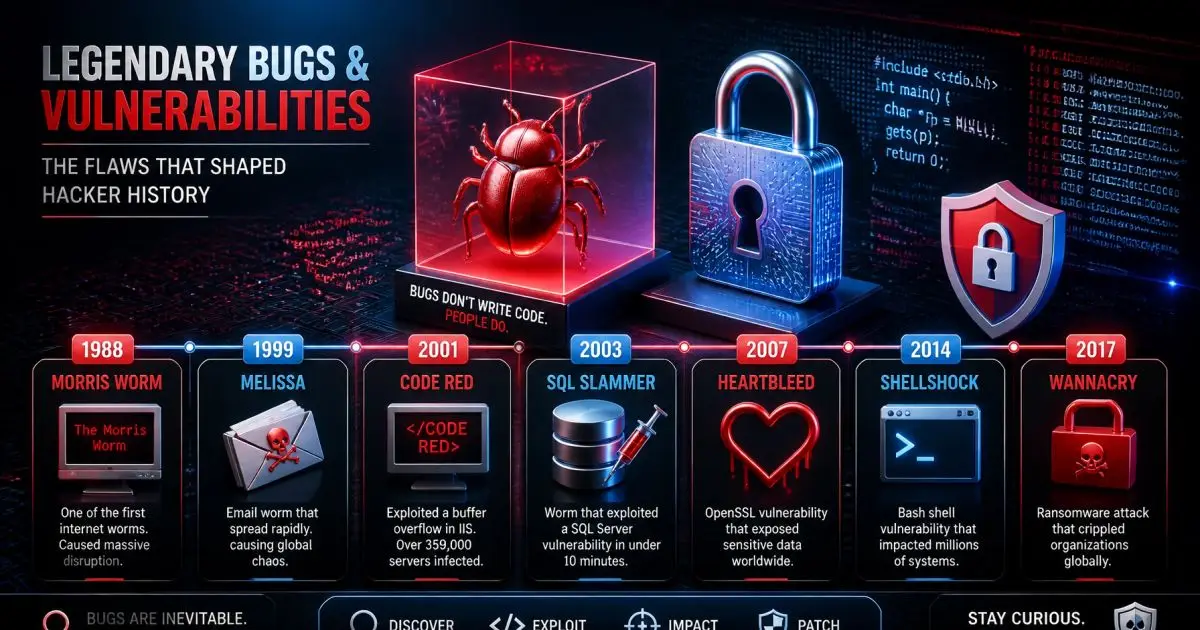
The Legendary Bugs That Shocked the World
If you want to understand how enterprise security actually improves, don't read vendor whitepapers. Look at the disclosures dropped on DEF CON stages over the years. These aren't theoretical vulnerabilities: they are earth-shattering bugs that forced entire industries to rewrite their playbooks.
1. Back Orifice (DEF CON 5, 1997)
The Cult of the Dead Cow (cDc) released Back Orifice on stage, a remote administration tool that could take complete control of Windows 95 machines over the internet. Microsoft was forced to respond to a security paradigm they hadn't anticipated: untrusted code execution on consumer endpoints.
2. ATM Jackpotting by Barnaby Jack (DEF CON 18, 2010)
Late security legend Barnaby Jack walked onto the DEF CON stage, plugged a cable into two different ATMs, and made them spit out cascades of cash on command without inserting a card ("Jackpotting"). It transformed physical ATM security overnight across the globe. The following year at Black Hat/DEF CON, he demonstrated wirelessly hacking insulin pumps to deliver lethal doses: proving that life safety devices were digital attack surfaces.
3. Hotel Keycard Cloning (2013)
Researcher Cody Brocious demonstrated in the Locksmith Village how a simple Arduino device plugged into the exposed programming port of standard electronic hotel door locks could open 1.6 million hotel rooms worldwide in seconds.
4. The Remote Jeep Cherokee Hack (DEF CON 23, 2015)
Charlie Miller and Chris Valasek showed the world how dangerous connected automobiles had become by remotely hijacking a Jeep Cherokee on a public highway: turning off the transmission, manipulating steering, and cutting brakes while a journalist was behind the wheel. The stunt triggered a recall of 1.5 million vehicles and changed automotive engineering forever.
5. Voting Machine Village & SOHO Router Contests
From the Voting Machine Village demonstrating how easily election hardware can be physically compromised, to EFF-sponsored SOHO router hacking contests uncovering dozens of zero-days in home gateways, DEF CON has consistently ripped the lid off systemic vulnerabilities before nation-states could exploit them in the wild.
Why DEF CON Is a Must-Attend Event
Think of DEF CON not as a lecture hall, but as a high-performance sports training camp combined with a tactical defense command center.
- The Villages: Whether it’s the Car Hacking Village, IoT Village, Aerospace, Biohacking, or Lockpick Village, you get hands-on access to the exact hardware infrastructure running our modern world.
- The Practitioner Mindset: Vendors sell silver bullets; hackers test reality. At DEF CON, the signal-to-noise ratio is pure technical truth.
- The Archives: If you couldn’t make it to Vegas this week, the community maintains the legendary DEF CON Media Archive, hosting decades of historical talks completely free.
If you're planning on attending — be sure to let us know so we can meet up!
Why It Matters
To keep an enterprise secure, leadership must understand that security is not a product you buy; it is a discipline you practice. Think of corporate IT infrastructure like a modern smart home: you can install the heaviest oak front door (perimeter firewall), but if you leave a sliding glass window unlocked in the back (an unpatched IoT device or third-party vendor API), the entire castle is compromised.
When researchers at DEF CON expose flaws in automobiles, routers, medical devices, and AI agents, they are showing us the exact threat vectors that sophisticated attackers will use against business supply chains tomorrow. Ignoring these disclosures is like ignoring weather warnings while sailing into a category 5 hurricane. Protecting your network integrity directly safeguards your operational uptime, client trust, and ultimately, your EBITDA.
How We Deliver It
At Proactive Risk, we translate the raw, cutting-edge threat intelligence born at conferences like DEF CON into battle-tested enterprise defense strategies for Morris County and New Jersey businesses.
We protect your organization through our comprehensive 8 layers of protection, ensuring no single point of failure can jeopardize your strategic goals:
- Perimeter Defense & Next-Gen Firewalls
- Endpoint Detection & Response (EDR / XDR)
- Identity & Access Management (MFA / Zero Trust)
- Email Security & Phishing Defense
- Continuous Vulnerability Management & CATSCAN® Assessments
- 24/7 Managed Security Operations (SOC)
- Employee Security Awareness Training
- Incident Response & Disaster Recovery Preparedness
Whether you need advanced vCISO advisory services, regulatory compliance frameworks (MEASURERISK covering HIPAA, CMMC, NIST, and NY DFS 500), or our proprietary CATSCAN® registered trademark vulnerability assessment, we ensure your organization stays steps ahead of emerging threats. For daily breach updates, legal obligations, and incident tracking, we encourage security leaders to monitor the Breach Intelligence Hub (also referenced as BREACHCLOCK.com).
Secure the future of your strategic goals.
PROACTIVE RISK
Intelligence-Led Cybersecurity & Risk Management
ANTICIPATE. DEFEND. PREVAIL.
36 First Avenue, Suite 203, Denville, NJ 07834
973-298-1160
proactiverisk.com