Your Employee Just Pasted Your Client List into an AI Tool. Now What?
An employee shares company data with an unapproved AI tool. Learn what to do next, how to uncover shadow AI, and six practical steps to govern AI use without slowing your team down.
By Tom Brennan
An employee is up against a deadline. They open a personal AI account, paste in a spreadsheet of clients, or a contract, pricing sheet, or sales pipeline, and ask for a quick summary.
The answer appears. The deadline gets closer.
Nothing breaks. No alarm goes off. No one calls.
That silence is the problem.
This usually starts with a busy person, not a bad actor
Most employees who turn to AI are trying to do their jobs faster. They use tools they already know from home, or they find a new assistant through a browser extension, an app, or a link shared by a colleague.
Your most capable people may also be your biggest ungoverned AI users. They see a practical way to save time, and may not know where the line is between helpful and risky.
A policy that only says “Don’t use AI” can drive the activity out of sight instead of managing it. That’s how shadow AI takes hold: people use tools the organization hasn’t reviewed, approved, or made visible.
The business question isn’t simply whether employees use AI. It’s whether they use it in ways your organization can see, secure, and account for.
What might be in the prompt?
A prompt may include customer records, contracts, source code, financials, employee information, or unreleased plans. It may contain far more than the employee intended to share.
When information goes into an AI service, it leaves the company’s direct control and is handled under that provider’s terms. Those terms, settings, and data practices can vary by service, account type, plan, and feature. Depending on the circumstances, content may be retained or used to improve services. Don’t assume that a personal account has the same safeguards as an organization-managed environment, or that deleting a chat proves every copy has been removed.
Nor should you assume that your company’s normal logging, data-loss prevention (DLP), or audit tools captured what happened. Coverage depends on how the service was accessed and what controls are in place. If the tool or account wasn’t approved, you may not have a reliable record of what data went where.
Start with the questions you can’t answer
For many organizations, the first finding isn’t that AI is inherently unsafe. It’s that basic governance questions have no clear answer:
- How many AI tools touch company data?
- Which ones have been reviewed and approved?
- What information can employees enter?
- Who owns the risk when an employee uses a tool for work?
- If something goes wrong, can you reconstruct what happened?
“We don’t know” is a useful starting point. It tells you where to focus.
If this just happened, take a measured first step
If an employee has already pasted company information into an unapproved tool, don’t panic, and don’t jump to conclusions about what the provider did with it.
Ask the employee to stop using that account or workflow for company information. Establish what was shared, when, through which tool and account, and whether the material included personal, confidential, regulated, or sensitive business data. Preserve the relevant details for review rather than treating deletion as proof that the issue is resolved.
Then involve the right people: your security or IT lead, privacy contact, and legal counsel as appropriate. Review the provider’s applicable terms and settings, along with relevant client contracts and internal policies. Notification duties depend on the data, circumstances, jurisdictions, and contractual obligations; get qualified guidance before deciding whether notice is required.
Six practical steps to close the governance gap
You don’t need a six-month program to make progress. Start with a focused review this week.
1. Find out what’s actually in use. Ask employees which AI tools they use for work and what tasks they use them for. A short, no-blame survey can surface tools that never reached IT. Where appropriate, review network egress, browser extensions, and software inventories too. Be clear about what you’re reviewing and why.
2. Write a short acceptable-use policy. Make it easy to understand: which tools are approved, what data is in bounds, what is off limits, and who can answer questions or review an exception. A one-page policy people can use beats a long document no one remembers.
3. Offer a sanctioned alternative. If employees need AI to do their work, give them a practical, approved way to use it. Otherwise, personal accounts can look like the path of least resistance. Set expectations about approved tools, features, and use cases; don’t assume that every plan or configuration provides the same protections.
4. Apply access and data controls. Use least privilege so tools and users can access only what they need. Require multifactor authentication. Where available and appropriate, consider managed accounts and tenant isolation. Check what the controls actually cover: a managed workspace does not automatically control AI use elsewhere.
5. Train people with realistic examples. Treat AI awareness like phishing awareness. Show employees how a harmless-looking request can expose a client list, contract clause, source-code snippet, or employee record. Give them a simple rule: if they’re unsure whether data can go into a tool, pause and ask.
6. Log and review what you can. Understand what activity records are available, what they capture, how long they’re kept, and who can review them. Logging coverage should be confirmed during setup; don’t treat a dashboard as proof that every AI interaction is visible. Review approved tools and usage periodically as your organization’s needs change.
Why it matters to the business
AI governance is risk management, but it’s also about protecting customer trust and supporting strategic goals. An insurance questionnaire may ask how AI use is governed. A client contract may set limits on where its data can go. State privacy laws, sector-specific requirements, and other regulatory expectations may be relevant to how information is handled. During a merger or acquisition, buyers may ask how the business controls its data and technology use. A clear, proportionate approach helps leaders answer those questions and make informed choices, without promising away risk.
How Proactive Risk can help
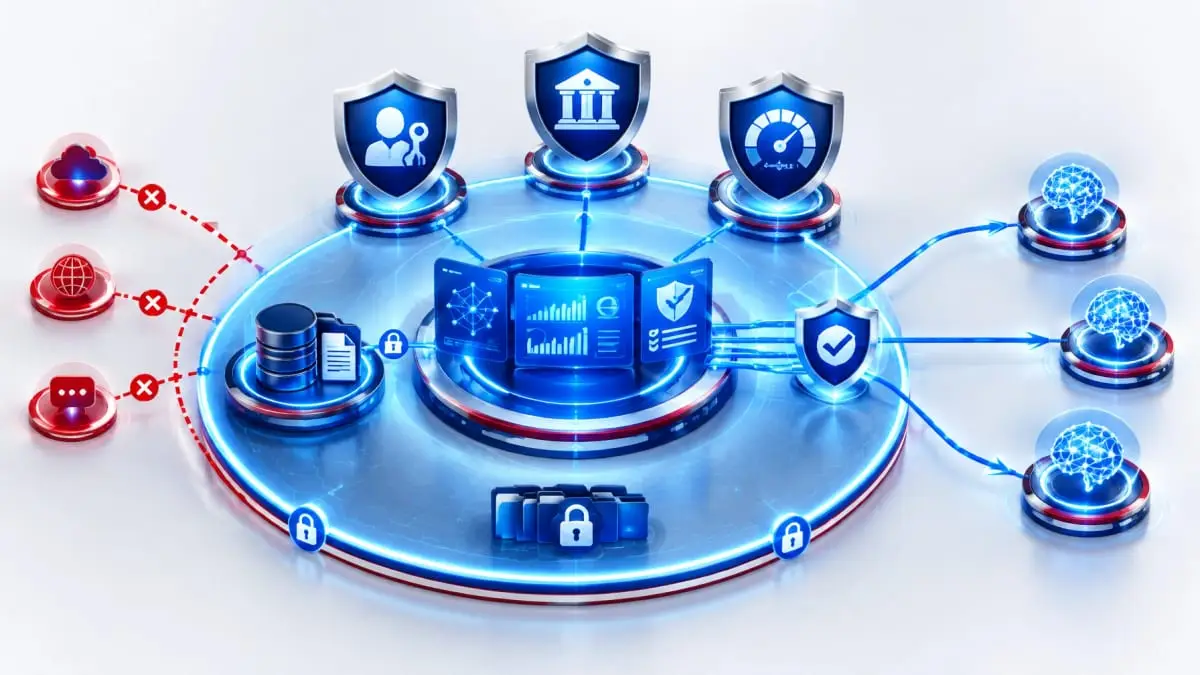
Proactive Risk’s GOVERNAI℠ helps organizations bring approved AI use into one managed workspace, powered by Hatz AI, with policy, access, and spend controls. Proactive Risk is a Microsoft partner and takes a Copilot-first approach: Microsoft 365 Copilot may be the right default for work inside Word, Excel, Outlook, and Teams, subject to eligible licensing, configuration, and Microsoft’s applicable data-protection terms.
GOVERNAI is intended to govern approved use of additional models beyond that Microsoft 365 use case. It does not automatically intercept or govern AI activity outside its workspace. Instead, it provides a managed environment for the work you choose to bring into it. Available audit trails and tenant-isolation controls can support oversight; logging coverage, retention, access, and provider processing are reviewed during setup.
An AI readiness assessment can help define policy, data-handling rules, and an adoption roadmap. Ongoing governance advisory can help keep those practices aligned as your needs evolve. Proactive Risk also offers FraudShield™ for deepfake and AI-fraud readiness, and CyberAdvisor℠ for ongoing risk oversight.
The takeaway
The question isn’t whether your people will use AI. It’s whether they’ll do it where you can see it.
Start by finding out what’s in use, setting clear rules, and giving people an approved way to get work done. That’s how you move from shadow AI to informed, accountable AI governance, and begin to See Around Corners™.
Schedule an Executive Risk Review
Start with a preliminary conversation based on what you share, not an audit, certification, or guarantee of compliance. Any paid work is scoped separately; managed services are optional.
Schedule an Executive Risk Review · Contact Proactive Risk · (973) 298-1160
Proactive Risk
Intelligence-Led Cybersecurity & Risk Management
Anticipate. Adapt. Overcome.
36 First Avenue, Suite 203, Denville, NJ 07834
973-298-1160 · proactiverisk.com